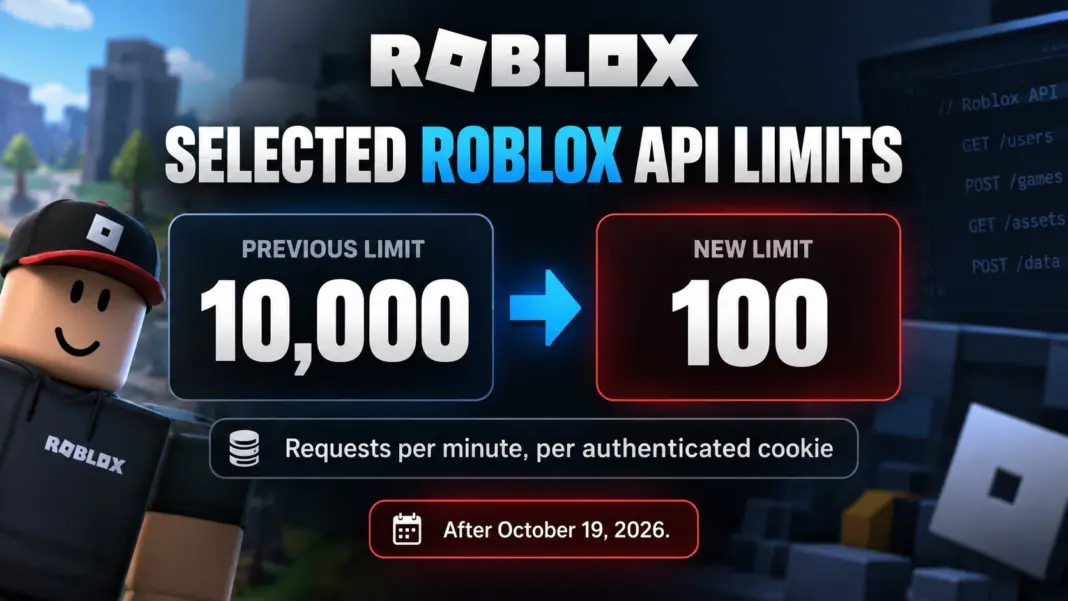
Roblox plans to cut selected web API limits from 10,000 requests per minute to 100 after October 19, 2026. Its published table also reveals a complication for developers: several affected endpoints have no listed Open Cloud alternative.
Roblox says the new ceilings exceed observed peak usage, so regular users should see minimal or no impact. Open Cloud limits remain unchanged. These APIs let software retrieve platform information, such as inventory details or images. The practical question is whether an outside tool can remain useful under a lower ceiling. Request patterns, caching and the information an application needs all matter.
Which Roblox API limits are changing?
Roblox’s September 30 API rate-limit announcement covers thumbnails, badges, inventory, users, game persistence and data stores. These examples all measure requests per authenticated cookie, per minute:
| Service and endpoint | Before | After | Listed Open Cloud alternative |
|---|---|---|---|
Thumbnails: /v1/bundles/thumbnails | 10,000/min | 100/min | None |
Inventory: /v1/users/{userId}/categories/favorites | 10,000/min | 100/min | None |
Thumbnails: /v1/batch | 10,000/min | 260/min | None |
Selected limits from Roblox’s announcement; each applies per authenticated cookie. A drop from 10,000 to 100 is a 99% reduction in the permitted request rate. Other rows use per-second or IP-based limits, so developers need to compare the units as well as the numbers.
Why moving to Open Cloud needs a closer look
Roblox’s Cloud API documentation already favours endpoints that support API keys or OAuth 2.0 authentication. It says legacy APIs using cookies can change without notice and carry weaker stability guarantees, making them a poor choice for production applications. Open Cloud supports operations such as updating games, restarting servers and managing data stores. It also offers inventory access. However, support for a broad category does not automatically make every older request interchangeable with a newer one.
The table’s “None” entries identify gaps in Roblox’s listed migration options. They do not prove that every alternative approach is impossible.
For a tool maker, migration requires checking what a replacement returns, which credentials it accepts and how many calls the same feature needs. Changing a URL is insufficient if the replacement lacks required information or handles records differently.
What lower limits could mean for players
The ecosystem extends beyond the Roblox games players launch to a marketplace where eligible Roblox Plus members can trade and resell items. Outside services that display platform information depend on being able to retrieve the data their features require. Consider a hypothetical inventory viewer that retrieves fresh information whenever someone opens a page. If demand exceeds its allowance, the developer might queue work, reuse a recent result or display an error. Those choices can affect how current or responsive the service feels; this example does not establish that any particular tool will fail.
A single page in an application can depend on several data requests, while some requests can retrieve information in batches. That is why an endpoint’s numerical limit cannot translate directly into a number of supported users. The tool’s implementation matters.
What developers can check before the rollout
Roblox’s rate-limit documentation explains how response headers can show the remaining allowance and reset window. It also documents HTTP 429, the response returned when requests encounter rate limiting.
Developers can compare recorded traffic with the relevant new ceiling, including short bursts that a daily average would conceal. Caching can reduce repeated fetches, while a request queue can spread work across the available window. Both approaches still require deciding how long users can reasonably wait for fresh information. Where the server supplies a Retry-After header, Roblox recommends using it to guide the next attempt. Otherwise, developers should retry with increasing delays. Repeatedly sending the same request immediately can add traffic without helping the user receive a result.
Authentication also affects how Open Cloud shares its allowance. API-key limits apply per owner, while OAuth 2.0 limits apply per access token. A migration therefore needs to account for how an application distributes requests across its users and credentials.
The useful test before the rollout is whether a service can still deliver its intended features within the new limits. That means checking realistic busy periods and the freshness of the data users actually see, then addressing any gap before it becomes a visible problem.